
Single sign-on is no longer just a convenience feature for SaaS companies. As organizations rely on more cloud applications across CRM, finance, analytics, and operations, managing disconnected passwords and inconsistent security policies becomes difficult to scale. That is why many teams are standardizing on Azure AD, now called Microsoft Entra ID, to centralize authentication and user lifecycle management across their SaaS stack.
If you are researching how to set up SSO for your SaaS team, the process usually focuses on four areas: selecting an identity provider, configuring SAML or OIDC authentication, enabling provisioning, and applying consistent security controls. This guide walks through those steps using MainFoundry’s Azure AD SSO integration as a practical example for modern SaaS environments.
Setting Up Azure AD SSO for SaaS Applications
For organizations already using Microsoft 365, Azure AD is typically the most practical identity provider because employees already authenticate through Microsoft services daily. That allows the same multi-factor authentication rules, device policies, and account lifecycle controls to extend directly into SaaS applications without creating additional operational overhead.
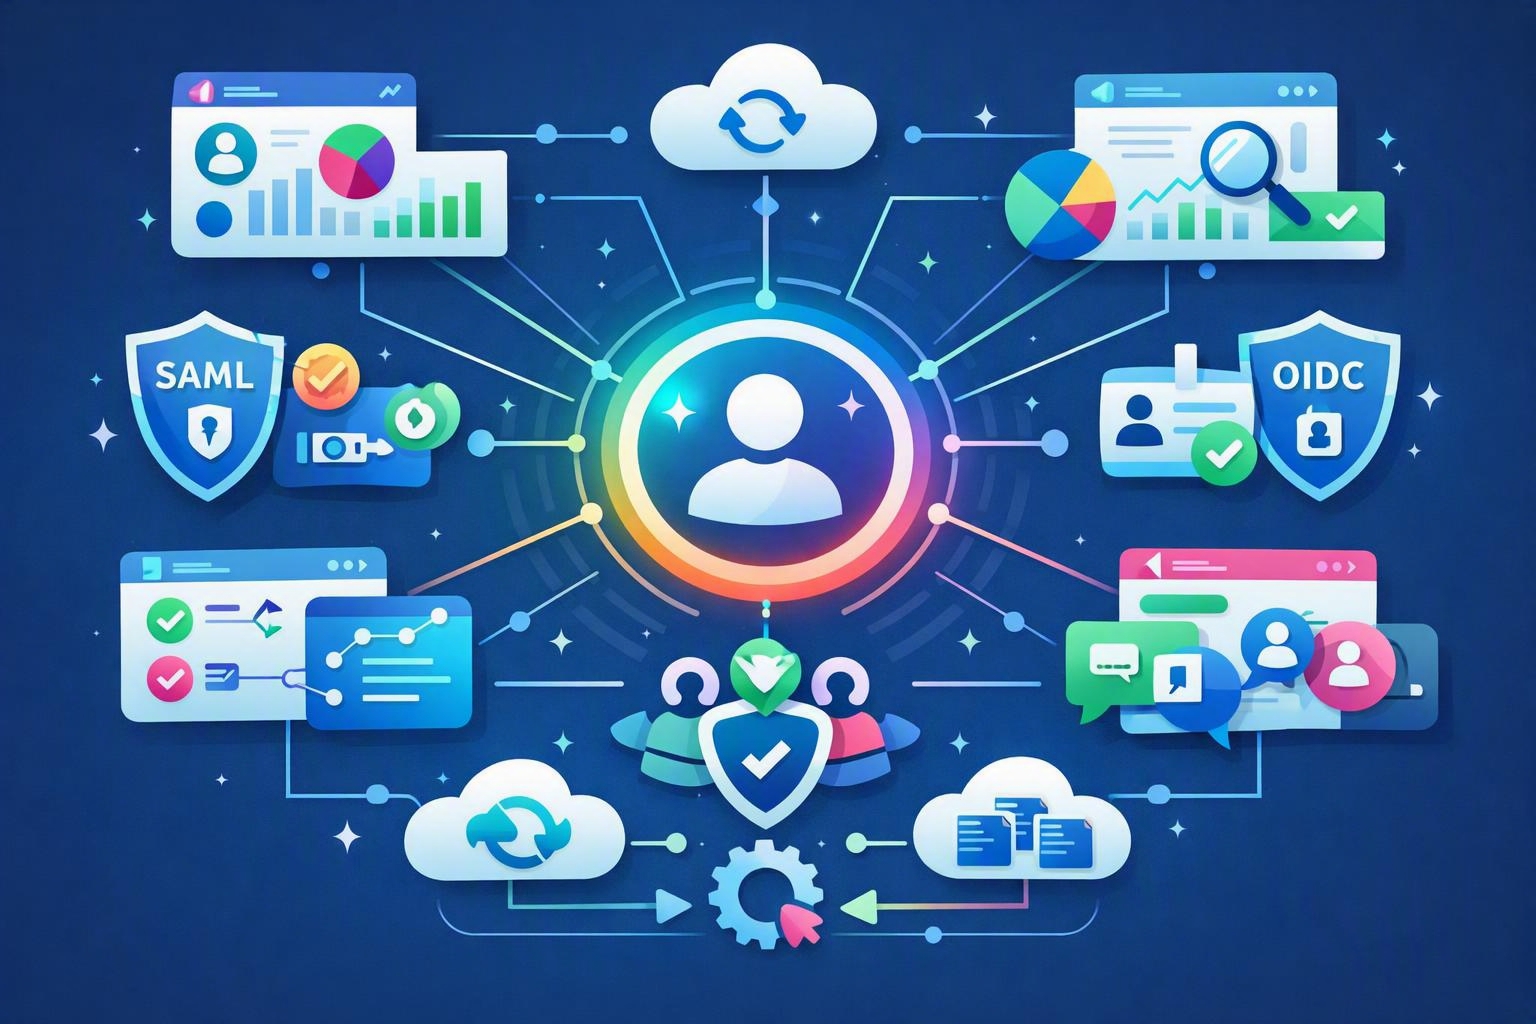
Azure AD supports both SAML 2.0 and OIDC. SAML remains common in enterprise environments because of its broad compatibility and maturity, while OIDC is often preferred for newer applications that rely on token-based authentication across web and mobile platforms.
A centralized identity layer reduces password fatigue, improves security visibility, and simplifies SaaS administration at scale.
Platforms such as MainFoundry combine CRM, finance operations, analytics, and collaborative workspaces into a unified environment. In systems like these, centralized authentication matters even more because one login can unlock customer records, billing information, internal documents, and operational workflows. Organizations using the unified CRM and customer management tools inside MainFoundry often mirror internal departments with Azure groups to simplify onboarding and permission management.
After choosing Azure AD as your identity provider, administrators create a new enterprise application inside Microsoft Entra ID. If the SaaS application is not listed in Microsoft’s gallery, a custom non-gallery application can be configured instead. Many teams create clearly named environments such as “MainFoundry-Production” and “MainFoundry-Sandbox” to reduce confusion later.
Most enterprise deployments still use SAML. In a standard SAML flow, Azure AD authenticates the user and sends a signed assertion to the SaaS platform. MainFoundry validates that assertion and establishes a secure session without requiring another password. Administrators configure values such as the Entity ID, Reply URL, and optional sign-on or logout endpoints to complete the trust relationship.
“Most SSO deployment issues happen around claims mapping and permissions, not the authentication protocol itself.”
Claims mapping is one of the most important setup steps because Azure AD must send user information in the exact format the SaaS platform expects. Many organizations use email addresses or user principal names as the unique identifier. MainFoundry also supports role-based access controls using Azure AD groups or custom attributes, allowing teams to centralize permissions for sales, finance, marketing, and operations.
Certificate management is equally important. Azure AD signs SAML assertions using a certificate, and MainFoundry must trust that certificate before authentication requests are accepted. Administrators typically import Azure federation metadata directly into the SaaS platform to establish secure communication between both systems.
Before a broad rollout, testing should happen with pilot users through Azure’s built-in “Test single sign-on” workflow. Many teams also validate the end-user experience through myapps.microsoft.com to confirm users can launch MainFoundry without additional credentials.
User Provisioning and Long-Term Security Strategy
Authentication alone does not solve identity management. Provisioning determines what users can access and how those permissions change over time. Many SaaS teams begin with just-in-time provisioning, where MainFoundry automatically creates accounts the first time someone signs in through Azure AD. Basic details such as email, department, and first name can be pulled directly from SAML or OIDC claims.
This approach works well for growing companies because new employees can gain access simply by joining the appropriate Azure AD group. Larger organizations, however, often prefer SCIM provisioning because it automates user creation, updates, and deactivation continuously. When employees change departments or leave the company, those changes automatically synchronize into MainFoundry.
Pro Tip: Plan Azure group structures before enabling SSO broadly. Consistent naming and role mapping make onboarding, deprovisioning, and compliance reporting significantly easier later.
Provisioning automation becomes especially important when organizations manage multiple operational systems through custom business workspaces or integrated finance and sales pipelines. Manual deprovisioning often creates orphaned accounts and unnecessary permissions that increase security risk.
A mature SSO deployment should extend beyond authentication itself. Strong SaaS identity strategies usually include MFA enforcement, Conditional Access policies based on device health or location, group-based authorization, automated lifecycle management, and audit logging across both Azure AD and the SaaS platform.
- Enable multi-factor authentication for all users accessing SaaS platforms.
- Use Azure AD groups to centralize departmental and role-based permissions.
- Automate provisioning and deprovisioning with SCIM whenever possible.
- Apply stricter Conditional Access rules to sensitive financial or administrative workflows.
Organizations using subscription and billing management features often apply stricter access policies for finance administrators handling invoicing, revenue reporting, or approvals. Security becomes easier to enforce when those policies are managed centrally in Azure AD rather than separately inside each SaaS product.
OIDC deployments follow many of the same principles as SAML, although they rely on token-based authentication instead of XML assertions. Administrators configure redirect URIs, client IDs, and token claims within Azure App Registrations. OIDC is particularly common for SaaS platforms that support APIs, mobile clients, or embedded workflows.
As organizations adopt AI-powered workflows, identity management becomes even more important. Features such as the AI assistant and workflow automation tools inside MainFoundry often interact with sensitive operational data across systems. Extending Azure AD policies into those workflows helps ensure only authorized users can access or automate critical business information.
Key Takeaways
The most effective SSO strategies treat identity as a centralized operational layer rather than an isolated login screen. Azure AD provides authentication, security enforcement, and lifecycle management, while platforms like MainFoundry extend those controls across CRM, finance, marketing, analytics, and operational workflows.
Before rolling out SSO broadly, validate claims mapping carefully, test group assignments thoroughly, and confirm your provisioning model can scale long term. Most implementation problems occur around permissions and lifecycle automation instead of the authentication protocol itself.
If your organization already relies on Microsoft 365, Azure AD SSO is usually the fastest path toward a secure and unified SaaS environment. To explore enterprise-ready operational workflows with centralized identity management, visit MainFoundry or contact the team directly at https://www.mainfoundry.com/contact.
Related Reading
Learn more about operational efficiency with unified CRM systems and scalable automation through custom business workspaces.